Developing an Enterprise Risk Governance Framework for Data Protection and Operational Resilience
Developing an Enterprise Risk Governance Framework for Data Protection and Operational Resilience
Executive Summary
A SaaS product planning initiative required structured risk identification, prioritization, and ongoing governance.
Webzenith Solutions prepared a risk and assumptions register addressing important business, operational, and technology risks, including data privacy and information security.
The resulting framework demonstrated how risk ownership, mitigation planning, monitoring indicators, and escalation procedures can be documented within a broader enterprise governance process.
Project Context
The initiative concerned a software platform where user adoption, service reliability, customer trust, and data protection could materially affect business viability.
Security risks were considered alongside product, commercial, and operational risks.
Risk Management Challenge
Organizations often document risks without defining how they will be managed.
A useful governance framework must distinguish:
- Risk severity and likelihood.
- Relevant business consequences.
- Responsible owners.
- Required preventive actions.
- Early warning indicators.
- Escalation thresholds.
- Monitoring frequency.
- Contingency procedures.
Documented Governance Approach
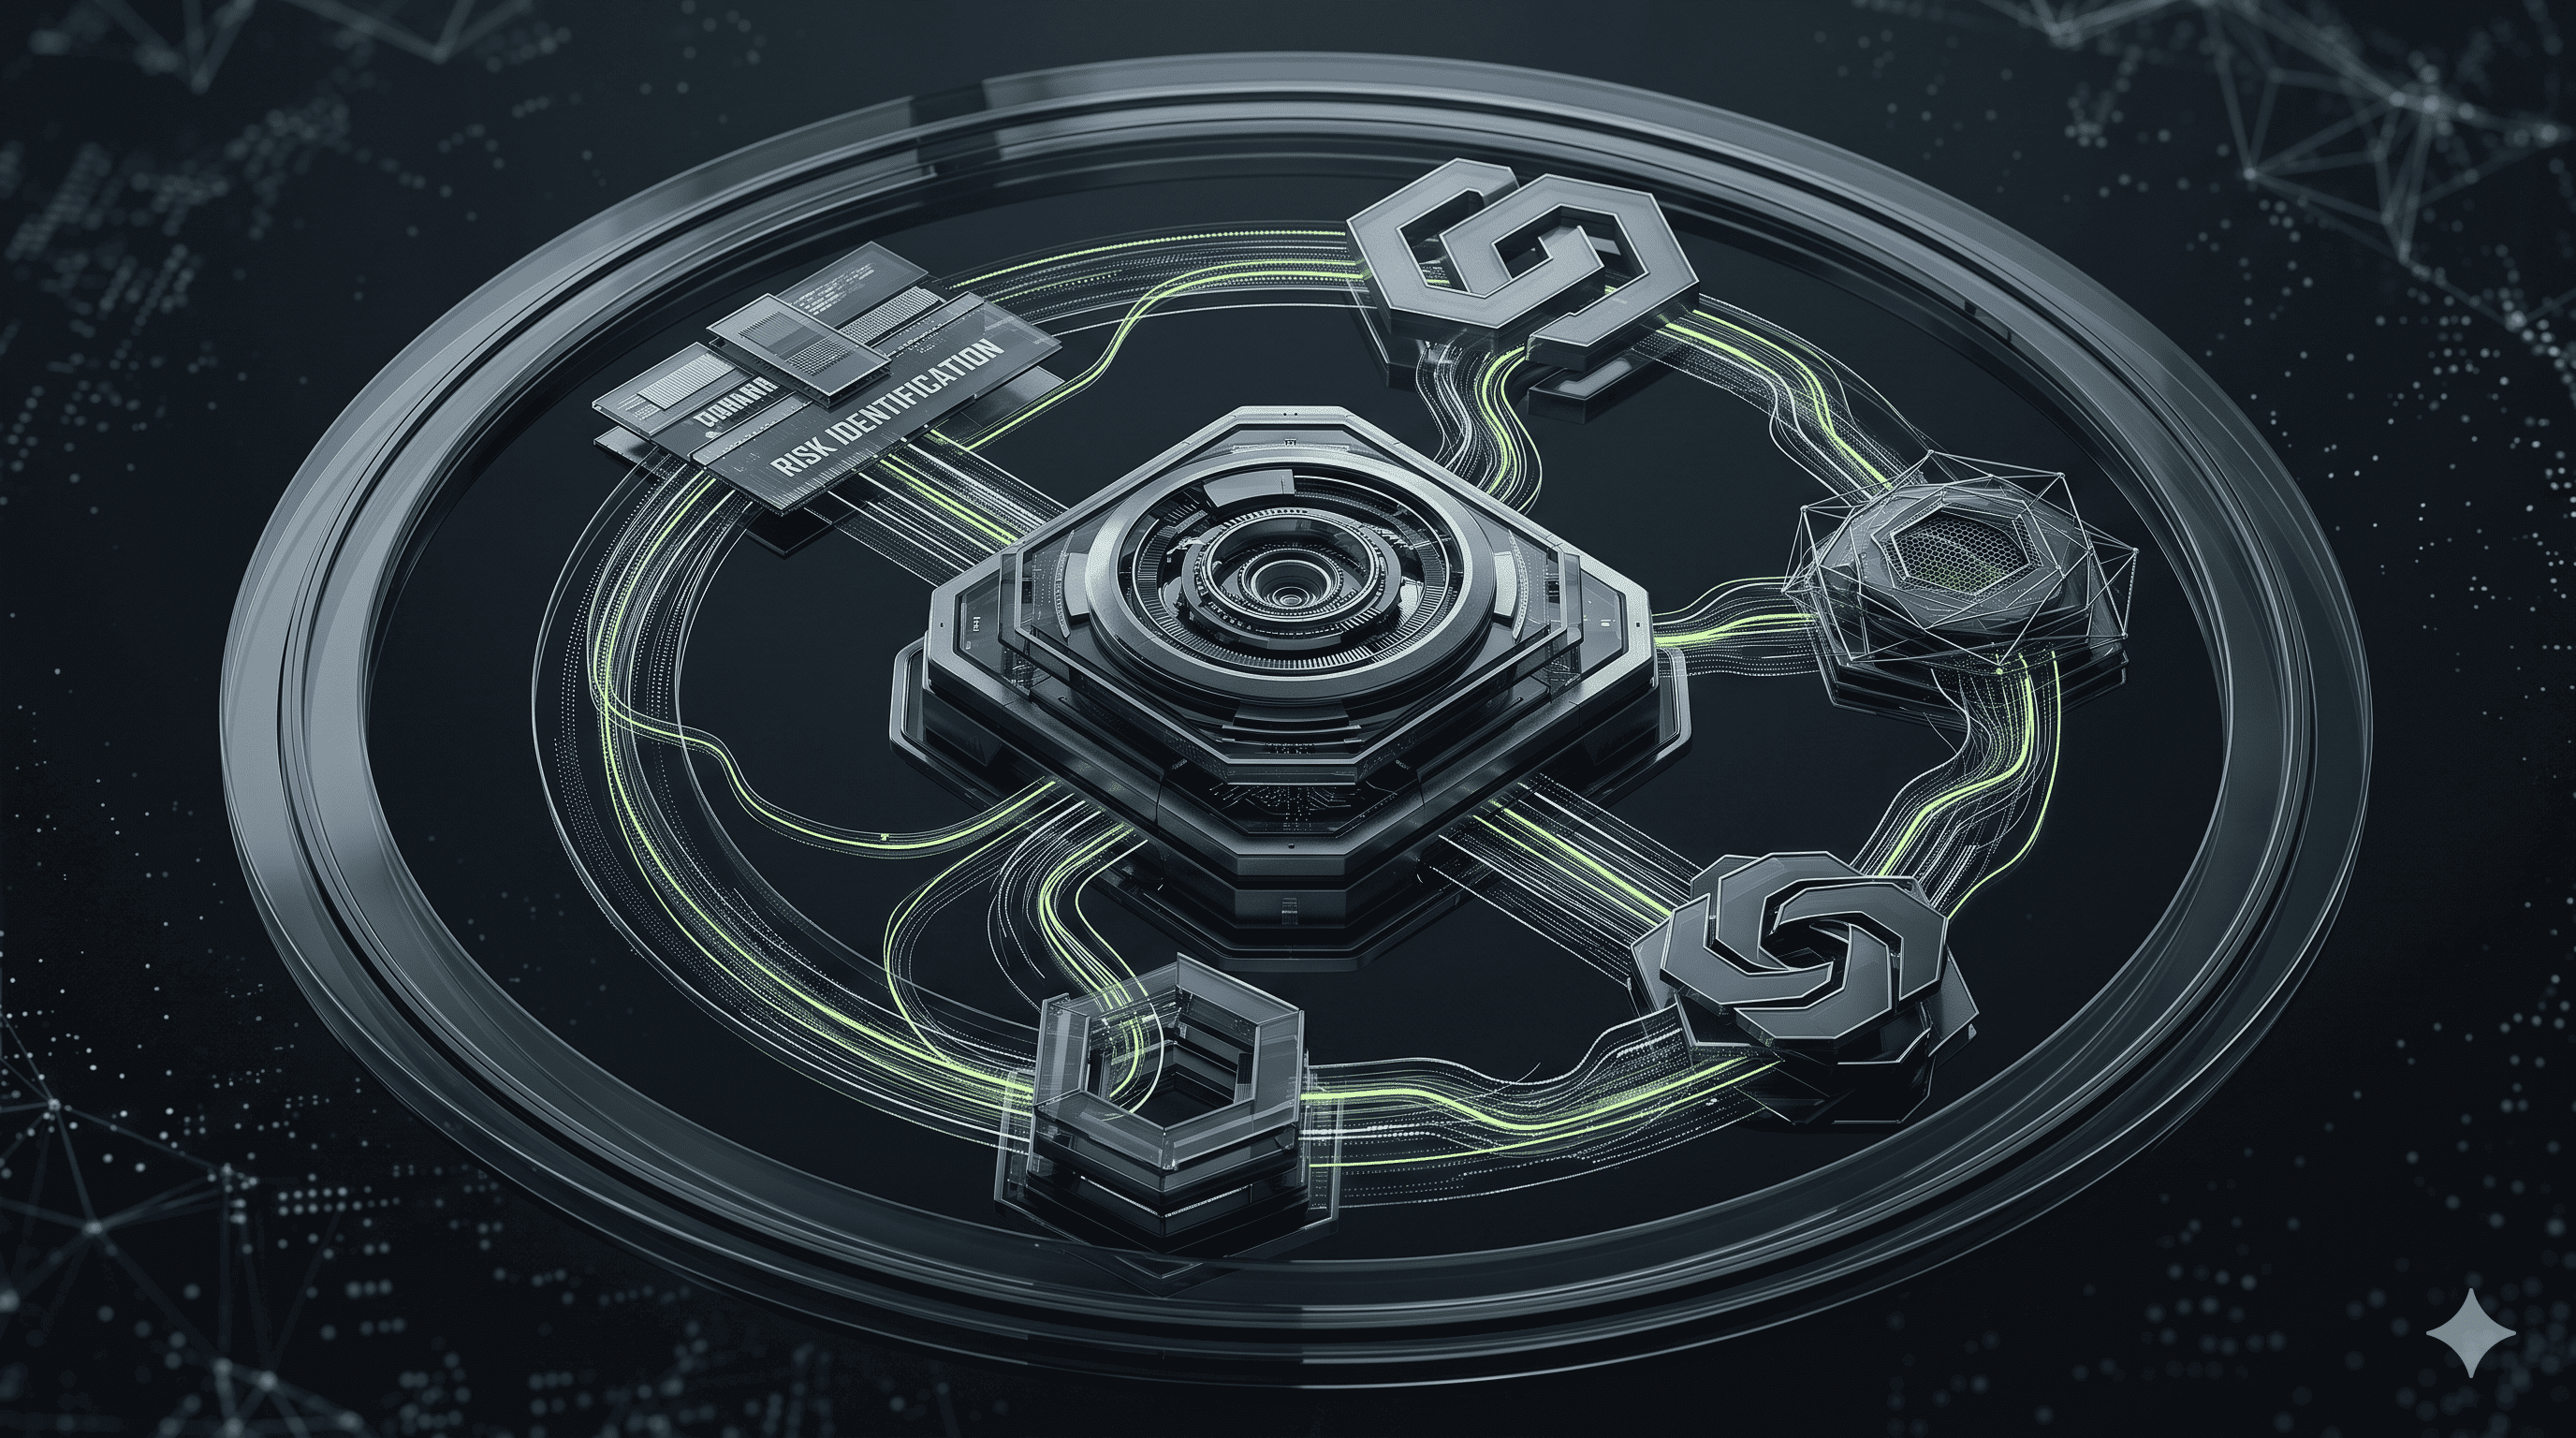
Risk Identification
The register documented material assumptions and identified categories of risk affecting the proposed product.
Severity & Likelihood Assessment
Risks were categorized using defined severity and likelihood considerations.
Data Protection Risk Planning
A potential data privacy breach was identified as a critical risk.
The document proposed mitigations including security controls, encryption, access management, audit logs, and future independent assurance activities.
Risk Ownership
Responsibility was allocated for monitoring and managing important risks.
Monitoring & Escalation
The governance document defined periodic reviews, key indicators, and escalation approaches appropriate to risk severity.
Business Value
The documented framework creates a structured basis for discussing risks, assigning accountability, and prioritizing mitigation work.
Proposed safeguards must not be confused with implemented security controls. Likewise, forecast breach probabilities and business outcomes are planning assumptions rather than validated predictions.
Conclusion
Security governance becomes more effective when organizations connect risk identification to accountable actions, monitoring, and operational decisions.
This initiative illustrates how a structured risk register can support a wider enterprise resilience program, while recognizing that operational security effectiveness requires actual implementation and ongoing assessment.
6 Security Service Areas
Readiness, HIPAA security, risk assessments, control implementation, vulnerability reviews, and audit support.
5 Engagement Stages
Assess, identify gaps, remediate, prepare, and maintain.
3 Frameworks Addressed
SOC 2, HIPAA Security Rule, and NIST Cybersecurity Framework.
2 SOC 2 Report Types Supported
Readiness preparation for Type I and Type II examinations.
CLIENT PERSPECTIVE
The Companies We Build With Say it
Better Than We Ever Could.
SOC 2 Readiness | Security Governance
Building a SOC 2 Readiness Roadmap Through Security Control Assessment and Audit Evidence Planning
SOC 2 Readiness | Security Governance
Building a SOC 2 Readiness Roadmap Through Security Control Assessment and Audit Evidence Planning
Healthcare Security | HIPAA Safeguards
Designing Secure Healthcare Messaging with Access Controls, Encryption and Audit Logging
Healthcare Security | HIPAA Safeguards
Designing Secure Healthcare Messaging with Access Controls, Encryption and Audit Logging
Clinical Research | Regulated Software Security
Engineering Compliance-Supporting Controls for a Multi-Tenant Clinical Trial Management Platform
Clinical Research | Regulated Software Security
Engineering Compliance-Supporting Controls for a Multi-Tenant Clinical Trial Management Platform
Application Security | Vulnerability Management
Assessing SaaS and API Security Through Access-Control Reviews and Risk-Based Remediation
Application Security | Vulnerability Management